
The Fake Version of Your Organization Is Already Online. Do You Know What It's Telling Your Customers?
Detection and response training for spoofed news articles, fake login portals, and impersonation domains built to deceive your customers and staff.
THREAT ARCHITECTURE
Attackers do not need to breach your network to steal your identity.
They build convincing clones of your customer-facing login portals, press rooms, and regulatory notices. These sites carry your branding, use typosquatted domains, and harvest credentials or spread false financial disclosures before your team notices.
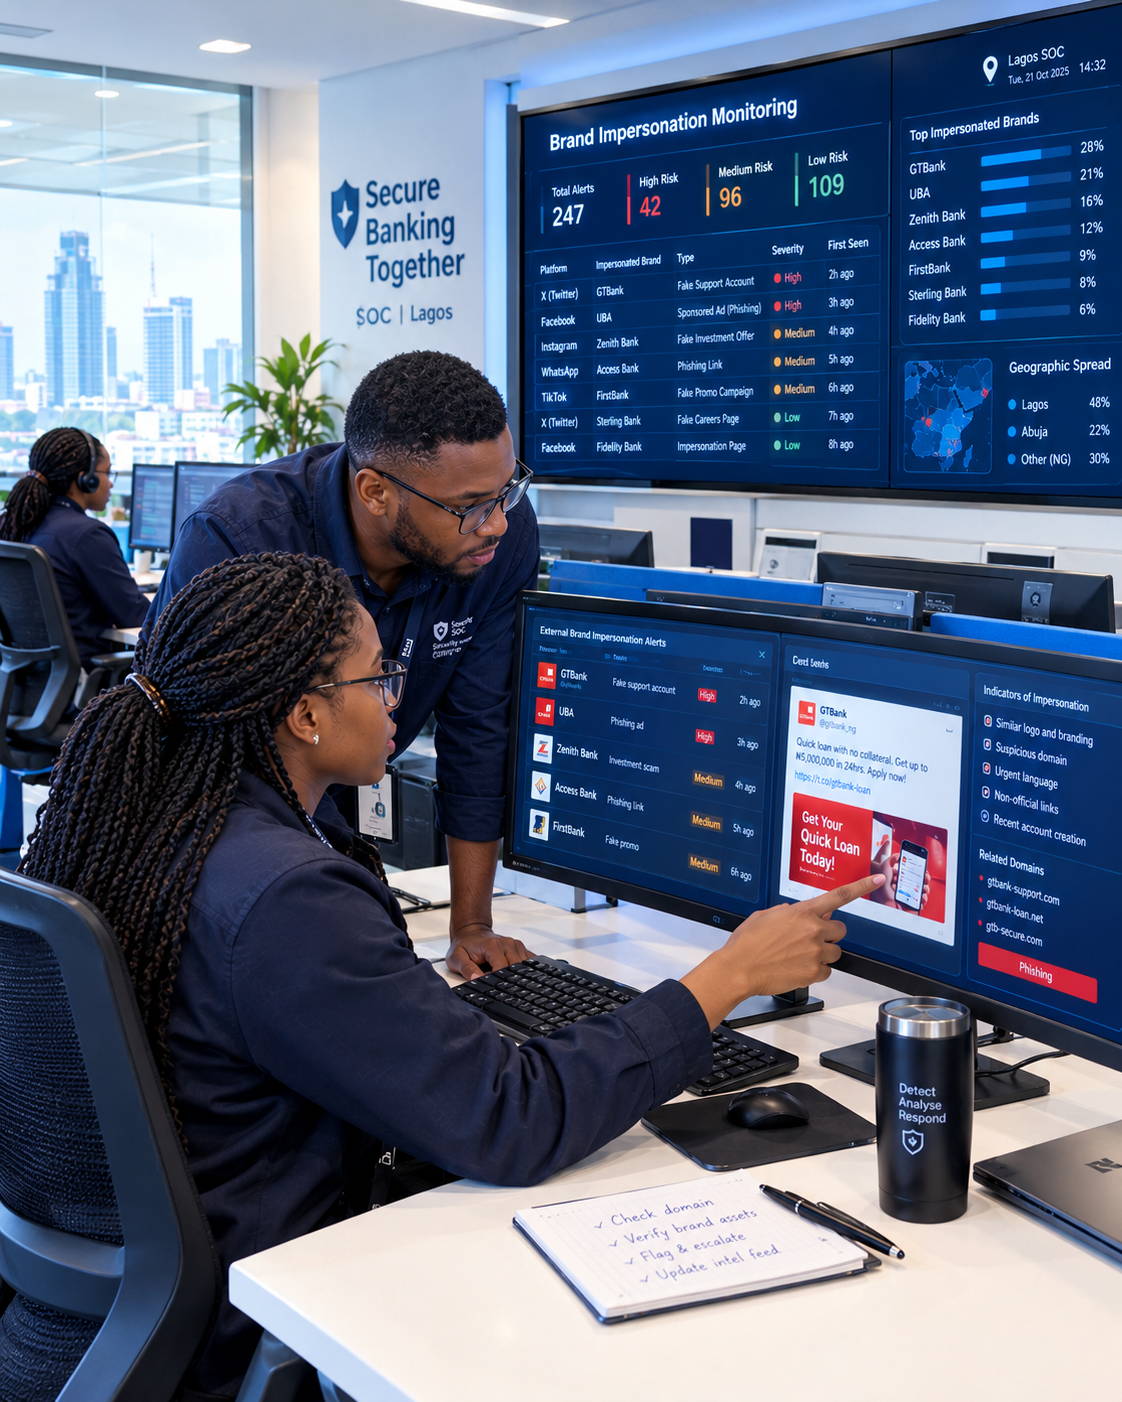
Sample indicator feed showing live monitoring vectors.
CORE DELIVERABLES
Four modules to lock down external brand protection.
Impersonation domain monitoring awareness
Trains security analysts to track newly registered domains leveraging brand names, misspellings, and international character variations.
Spoofed portal recognition training
Teaches staff and digital channels teams how to spot subtle layout flaws, manipulated SSL certificates, and credential-harvesting hooks.
Fake news article response protocol
Establishes an internal workflow for verifying, escalating, and refuting malicious disinformation before market impact occurs.
Customer communication templates
Pre-approved messaging frameworks to alert users safely without causing panic or validating the fraudulent portal.
COMPARATIVE RISK PROFILE
Why technical takedowns alone fail without staff readiness.
Domain registrars and hosting providers take hours or days to answer abuse complaints. In that window, customers land on fake portals. Your team must be trained to respond while legal processes run.
Domain blocklists and waiting
- Relies entirely on external registrar speed.
- Customers exposed during reporting lag.
- No internal protocol for handling impacted users.
Detection training and rapid protocol
- Identified within minutes of publication.
- Standardised internal escalation path.
- Pre-cleared customer communications ready.
IMPLEMENTATION TIMELINE
From surface scanning to a tested response protocol.
A structured rollout that integrates monitoring oversight with your communications and legal teams.
Scope and asset mapping
Identify critical public domains, brand variations, and executive names requiring ongoing external surveillance.
Protocol customisation
Build custom escalation paths connecting IT security, legal counsel, and corporate communications.
Workforce simulation
Test staff ability to identify spoofed landing pages and execute reporting procedures accurately.
Governance review
Align reporting mechanisms with requirements under ISO/IEC 27001 and the CBN cybersecurity framework.
TARGET SECTORS
Built for organisations where trust is the primary attack surface.
If your customers authenticate online, transfer funds, or rely on official announcements for financial decisions, malicious portals present an immediate operational risk.
Relevant compliance frameworks include ISO/IEC 27001, the CBN cybersecurity framework, and the NDPA 2023 enforced by the NDPC.
Frequently asked questions
Does this include takedown services for spoofed domains?
This service focuses on detection training and response protocol; domain takedown execution may require coordination with your legal team or a specialised takedown provider, which we can help identify.
How quickly can a spoofed news portal spread false information?
Amplified by social media channels, fake news articles can reach key stakeholders and customers within minutes, making internal detection speed critical.
Does this integrate with existing security operations tools?
Yes, the response protocols are designed to plug directly into existing security incident response and communication workflows.
Neutralize spoofed news portals and impersonation domains through the ProtectYourData platform. See how the training works.
See how the training works →